SaaS Pricing Strategy for the US Market
August 15, 2025
Positioning and Messaging for European SaaS Entering the US Market
October 15, 2025
SOC 2 for European SaaS Companies Selling to US Enterprise Buyers
Your ISO 27001 certificate is real, current, and won’t move a single US enterprise deal past security review. That’s not a knock on the standard — it’s a mismatch of markets.
Why US Enterprise Buyers Ask for SOC 2 (Not ISO 27001)
SOC 2 is a US-born standard — developed by the American Institute of Certified Public Accountants (AICPA) — and it became the default assumption baked into American procurement long before most European vendors were selling into the US at all. When a security reviewer at a US enterprise opens a vendor questionnaire, “Do you have a SOC 2 Type II?” is often the first question, not one of many.
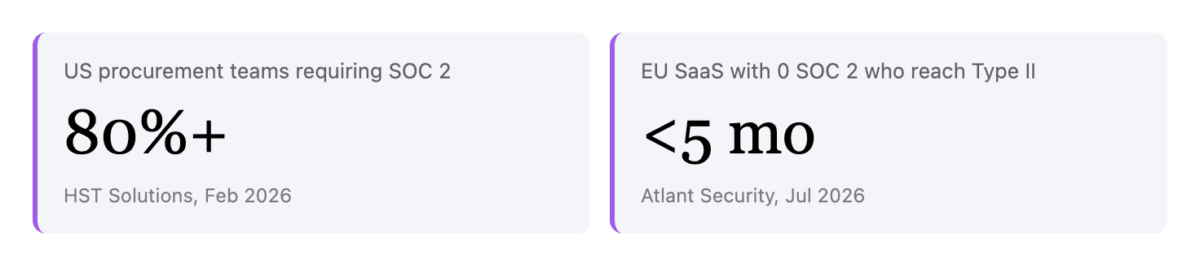
Over 80 percent of US enterprise procurement teams require a SOC 2 report before a vendor clears security review. Many European teams are surprised that a well-respected, globally recognized ISO 27001 certification isn’t automatically enough — US security teams frequently ask for SOC 2 specifically, even when ISO 27001 is already in place.
SOC 2 vs ISO 27001 vs GDPR: What Covers What
These three get treated as interchangeable in a lot of vendor conversations, and they aren’t. SOC 2 is an AICPA attestation, built around five Trust Services Criteria — security, availability, processing integrity, confidentiality, and privacy — and audited by a CPA firm. ISO 27001 is an international certification for information security management systems, prescribing 93 specific controls across four domains. GDPR is neither an attestation nor a certification — it’s a binding EU regulation on how you handle personal data, with no revenue threshold and no opt-out.
The controls overlap substantially, which is the useful part: achieving one makes the next meaningfully faster, since you’re extending an existing program rather than starting from scratch. But none substitutes for another in a procurement conversation. If your primary market is the US, prioritize SOC 2. If you’re selling into Europe, the Middle East, or Asia-Pacific, ISO 27001 may be requested first. Companies serious about both markets typically end up maintaining both — not because it’s redundant, but because each is the specific artifact a specific buyer’s legal team is trained to look for.
Type I vs Type II: What US Procurement Actually Requires
Not all SOC 2 reports mean the same thing to a buyer, and the difference determines how long your sales cycle actually is.
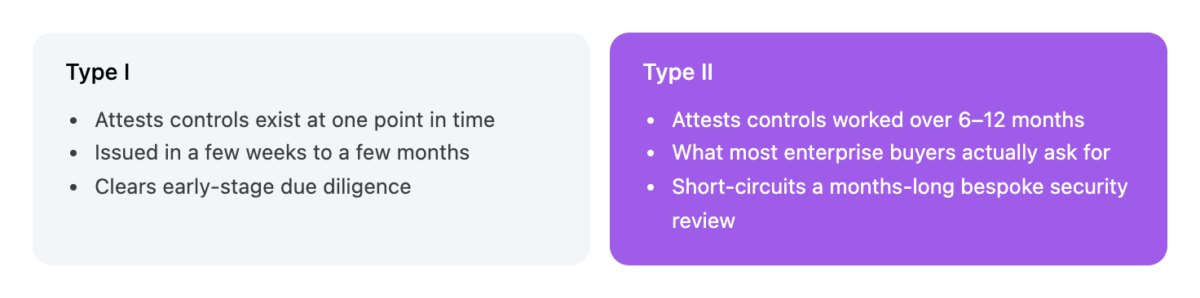
A Type I attests that your controls exist at a single moment; a Type II attests that they operated effectively over an observation period, usually six to twelve months. Many vendors ship a Type I first, mainly to have something concrete to hand a customer while the Type II observation window runs. But enterprise buyers ask for Type II specifically — a current Type II report replaces months of bespoke security review with a thirty-minute conversation about the auditor’s findings. Without one, you’re back to answering the same long-form questionnaire, deal after deal, which is exactly the kind of friction that turns into a stalled procurement process well after pricing and terms are already agreed.
Building Your Trust Page Before Your First US Enterprise Deal
You don’t need to wait for the report to land before you start building the page that presents it.
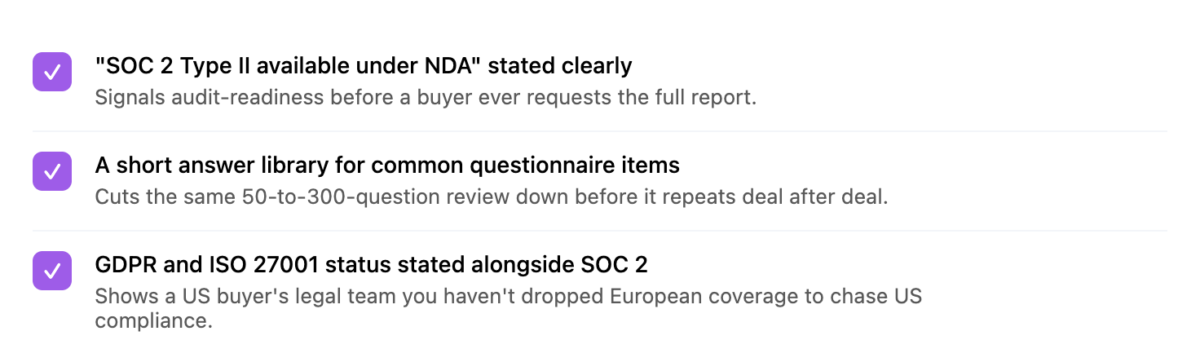
None of this requires the audit to be finished. Publishing “SOC 2 Type II available under NDA,” even while your Type I is still the current report, sets the expectation correctly and gives your sales team language to use the moment a buyer’s security team gets involved — which, per the pattern we cover in why enterprise deals stall in US procurement, is often well after pricing is already agreed.
Timeline and Cost: What to Budget Before You Sell
A first-time SOC 2 Type II report typically runs six to twelve months from kickoff to issued report, dominated by remediation work and the mandatory observation period rather than the audit itself. A Type I can be issued in a few weeks to a few months, which is why most first-time programs ship one before the Type II clock even starts. European teams starting from an existing GDPR or ISO 27001 program tend to move faster than that: Atlant Security reports EU SaaS companies going from zero SOC 2 coverage to a full Type II in under five months, largely because the underlying controls — encryption, access management, incident response, vendor risk — already existed under the other frameworks and didn’t need to be built twice.
Budget for both time and reuse. The first framework is the expensive one to stand up; each subsequent one — SOC 2 after ISO 27001, or vice versa — mostly extends work you’ve already paid for once. Building that reuse into your compliance roadmap, alongside the trust and pricing signals we cover in the European SaaS valuation gap, is what turns SOC 2 from a line item into a deal-closer.
ABOUT THE AUTHOR
Written by Luca Lundgren, Founder at Demand Scalers. Luca has five years of demand generation experience working with companies like Simplex Wireless and Dentsu, and holds a Master’s in Marketing from Aalto University.